Safe Governance: Why Deterministic Guardrails Are Mandatory for AI
A model that is usually careful is not a control. If AI can touch your plan, the safety has to live in code that does not care what the model "meant". Here are the gates built into CoMng.AI.
AI that edits your project needs deterministic guardrails: rules enforced in code, not in a prompt. CoMng.AI requires approval before any AI-drafted change is applied, flags requests that touch five or more objects as bulk changes, scopes agent API keys, and records actions in audit logs.
- Humans approve, AI proposes: ARI never applies a change itself; applying requires an Approved change request.
- Bulk changes are flagged by code: a request that touches five or more objects with the same action is flagged, marked Critical and carries a warning.
- Agents get least privilege: API keys carry per-action permissions, project scope, rate limits, expiry and IP whitelists.
- Everything is logged: applied changes and meaningful actions appear in the audit log.
A Model Is Not a Control
Language models are good at following instructions most of the time. "Most of the time" is acceptable for drafting a status paragraph and unacceptable for deleting tasks. A safety rule that exists only as a line in a prompt is a suggestion; a safety rule that exists in code is a gate.
The design principle in CoMng.AI is that AI may propose anything but may only change things through paths that have deterministic checks and a human decision.
Four Gates Between AI and Your Plan
Gate 1: Propose, never apply
ARI drafts change requests, but the apply action requires the request to be in Approved status. The model has no path that skips this.
Gate 2: Bulk-change detection in code
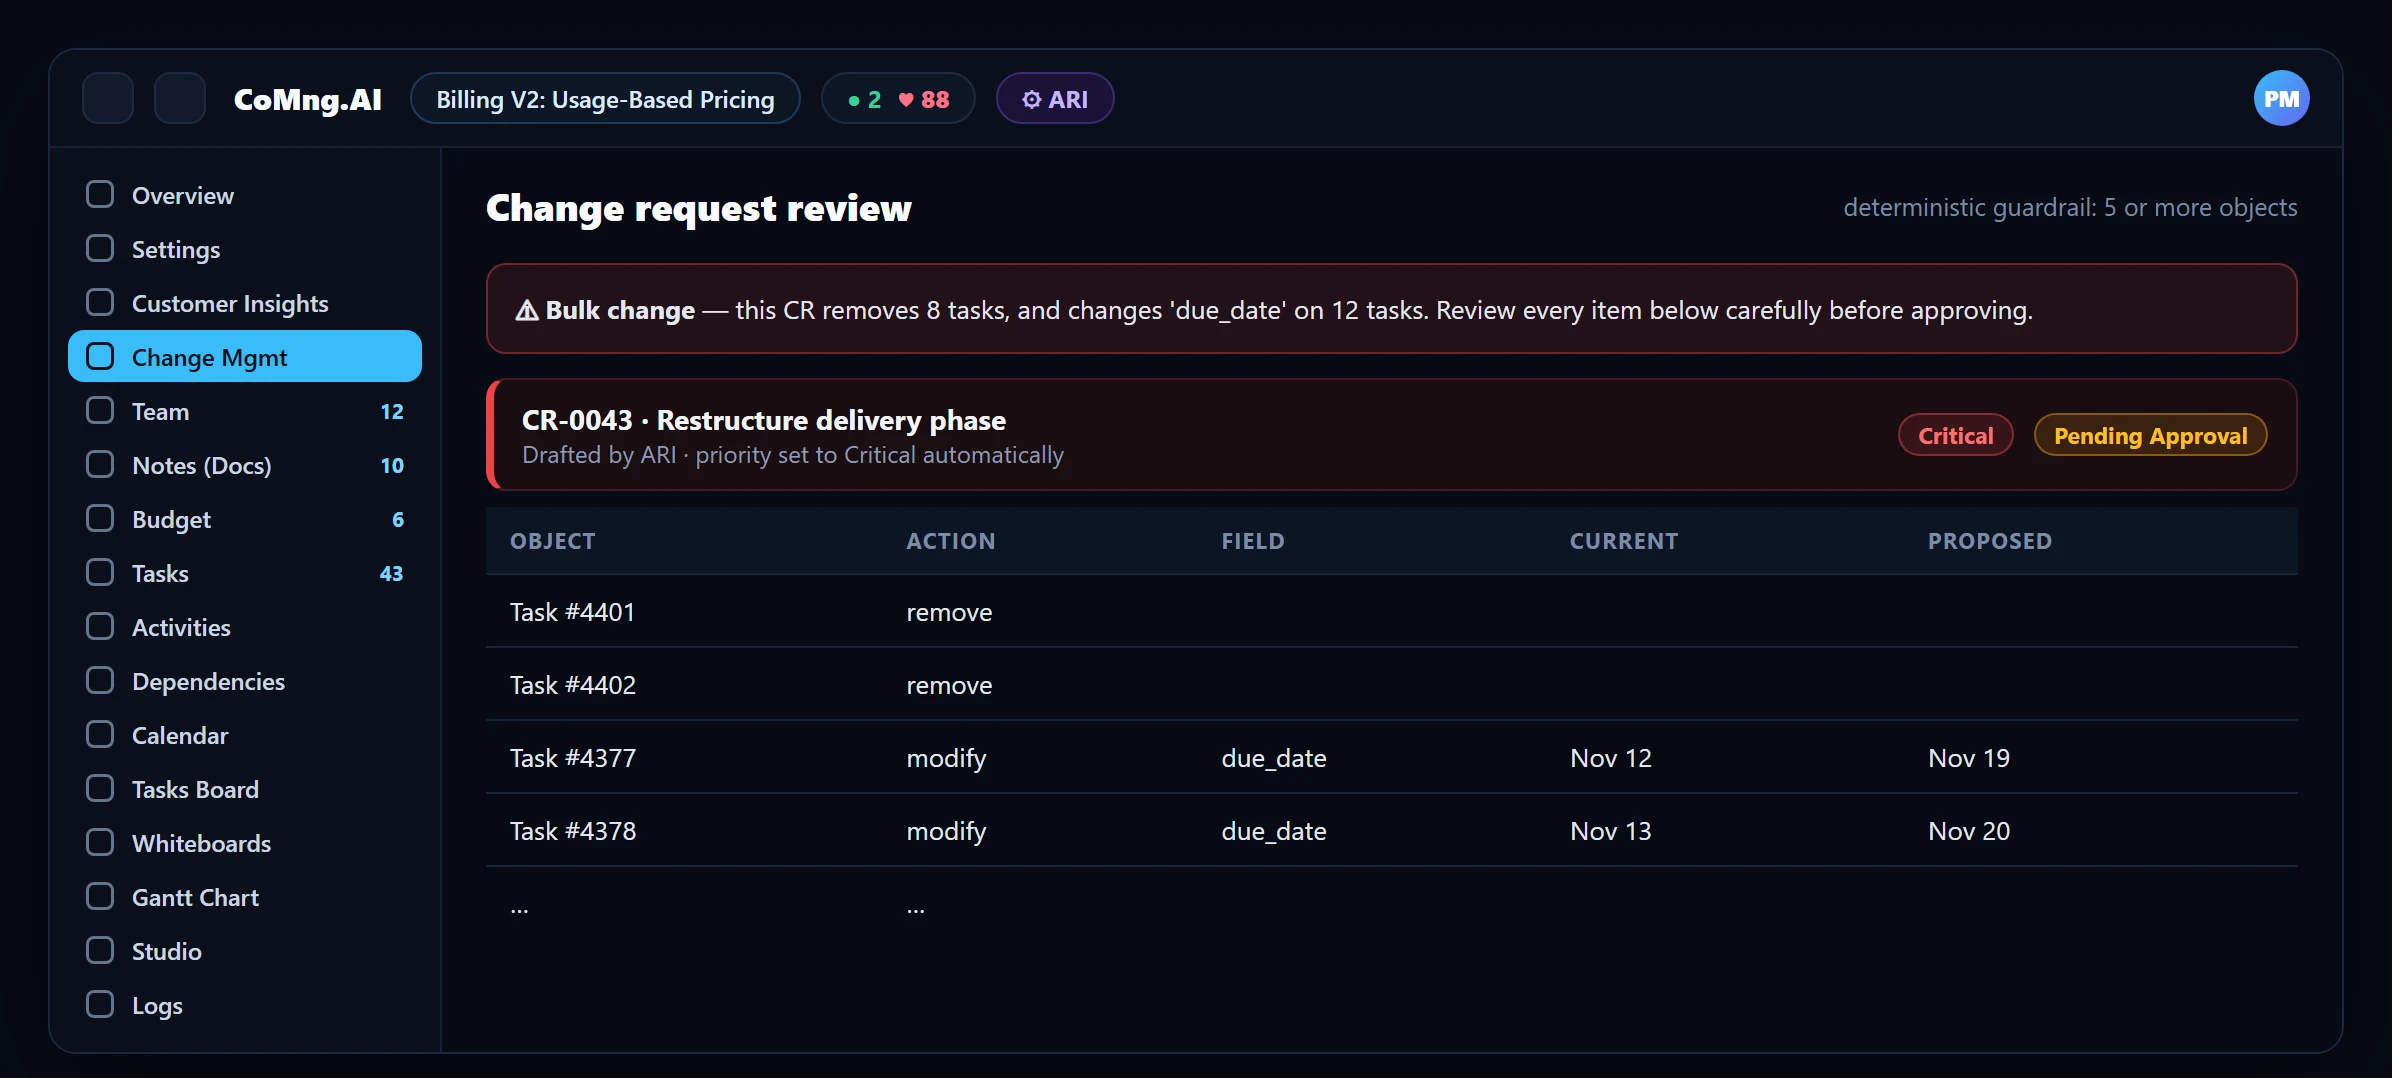
When a drafted request removes five or more objects of one type, or changes the same field on five or more objects, the platform computes that from the saved items, not from the model's own judgment. It adds a warning ("Bulk change: this request removes 8 tasks... Review every item carefully before approving") and sets the priority to Critical.
Gate 3: Scoped credentials
External agents connect with API keys whose permissions, projects, rate limits, expiry and IP whitelist you set. MCP uses the same key and enforces its exact limits; it grants nothing extra.
Gate 4: Audit trail
Applied changes, who applied them and when are recorded in the filterable Audit Logs, alongside the change request history.
The Sandbox Makes Approval Informed
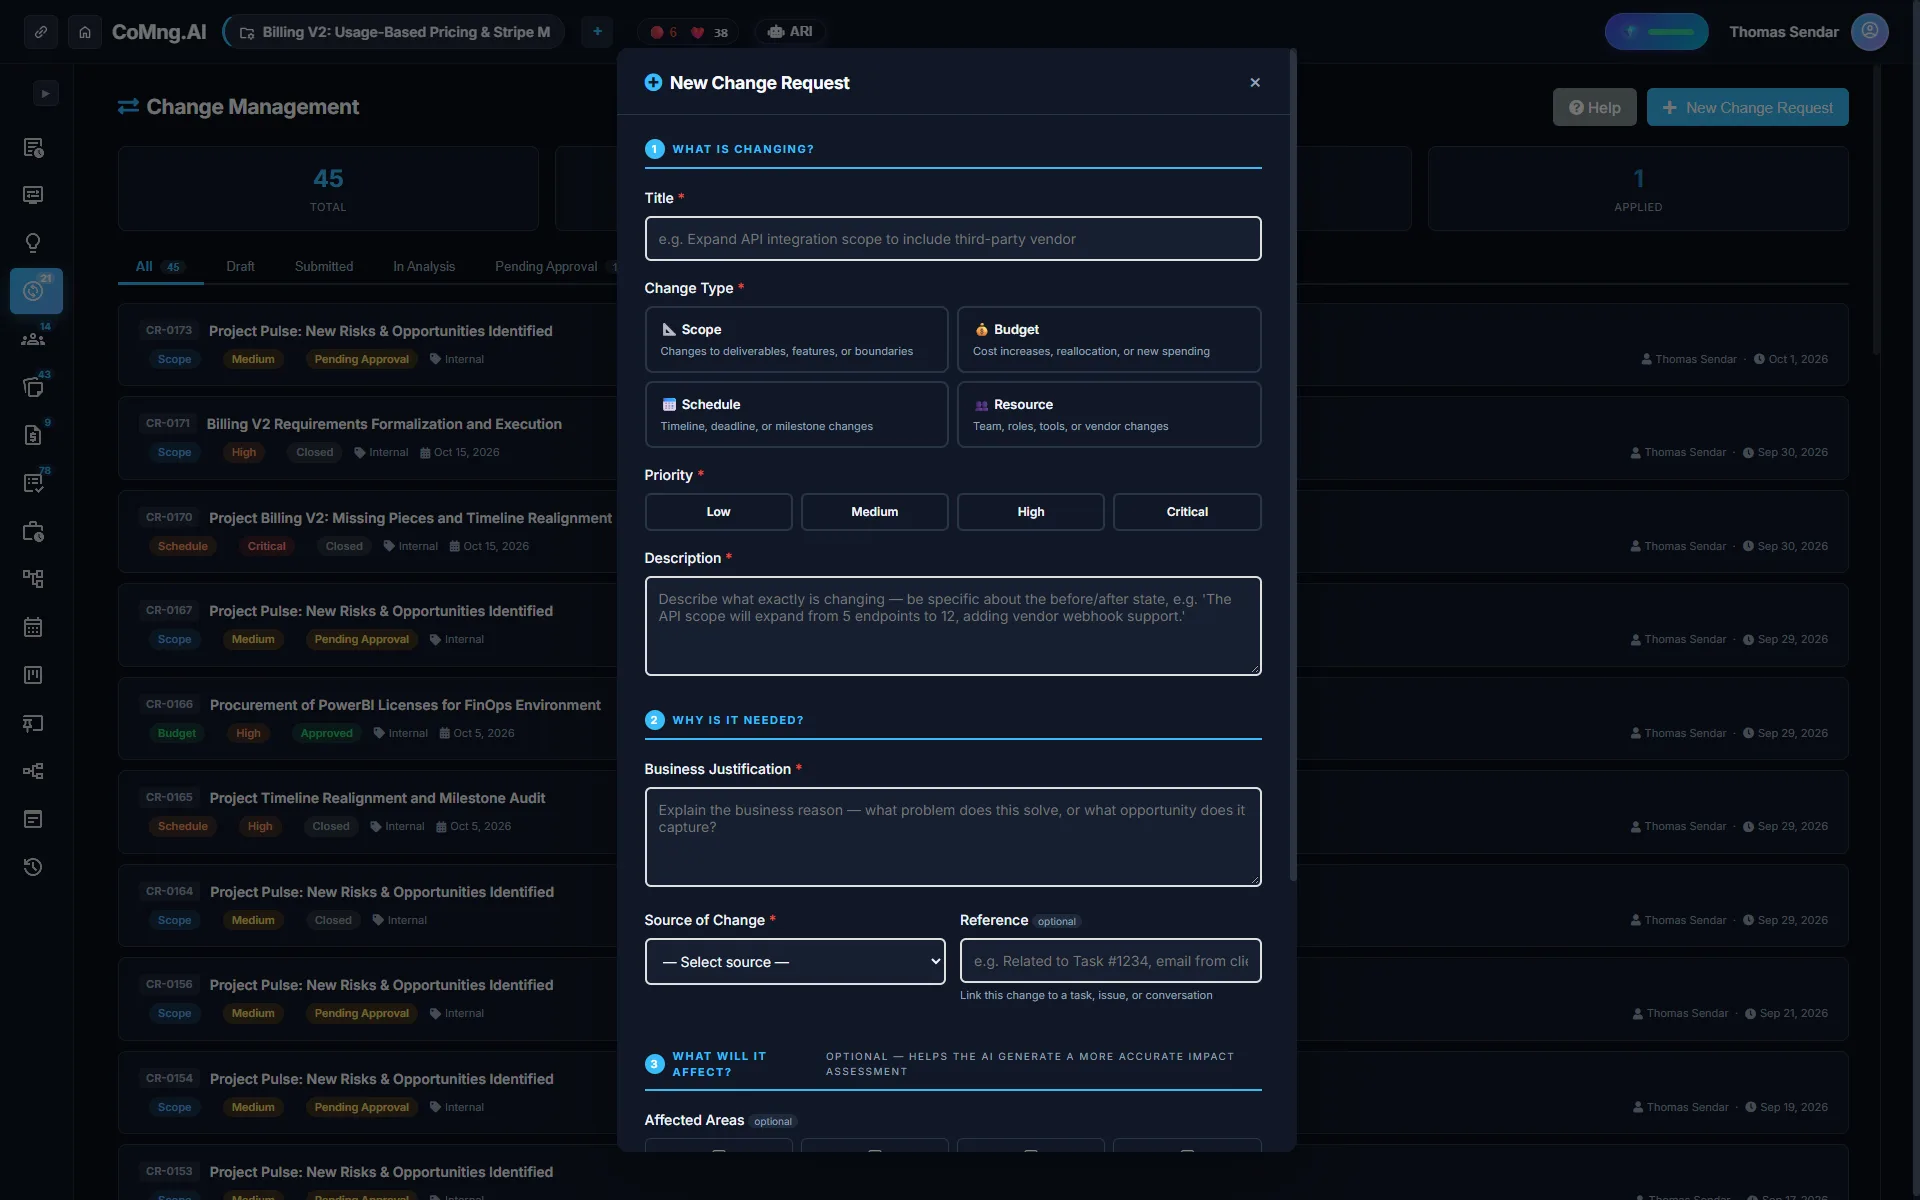
Approval is only a gate if the approver can see what they are approving. Each change request has a sandbox preview showing current and proposed values for every affected object, side by side. A reviewer can approve everything, apply item by item, or reject. See Change Request Impact Assessment.
One Pattern Everywhere: Auto Apply or Change Request
The same safety choice appears across CoMng.AI's AI generators. When you run the AI Task Builder, AI Brief or Optimize Timeline, you choose how the result is handled: Auto Apply writes it into the project immediately, while Change Request (or Create Change Request) saves it as a pending request for review and approval. Import Tasks always takes the change-request route. Use Auto Apply for low-risk work on a draft plan, and the change-request mode once the plan is committed.
Least Privilege for Humans, Integrations and Agents
Whether the caller is a script or an autonomous coding agent, it connects through an API key created by an Admin. The key scopes what it can do and where from:
- Projects: specific projects, or all projects.
- Access level and actions: read only, insert only or read and insert, refined by per-action checkboxes (list tasks, create task, update task, delete task and so on).
- Rate limits: per key; exceeding them returns HTTP 429.
- Expiry: an optional date after which the key is rejected.
- IP whitelist: requests from other addresses are rejected with HTTP 403.
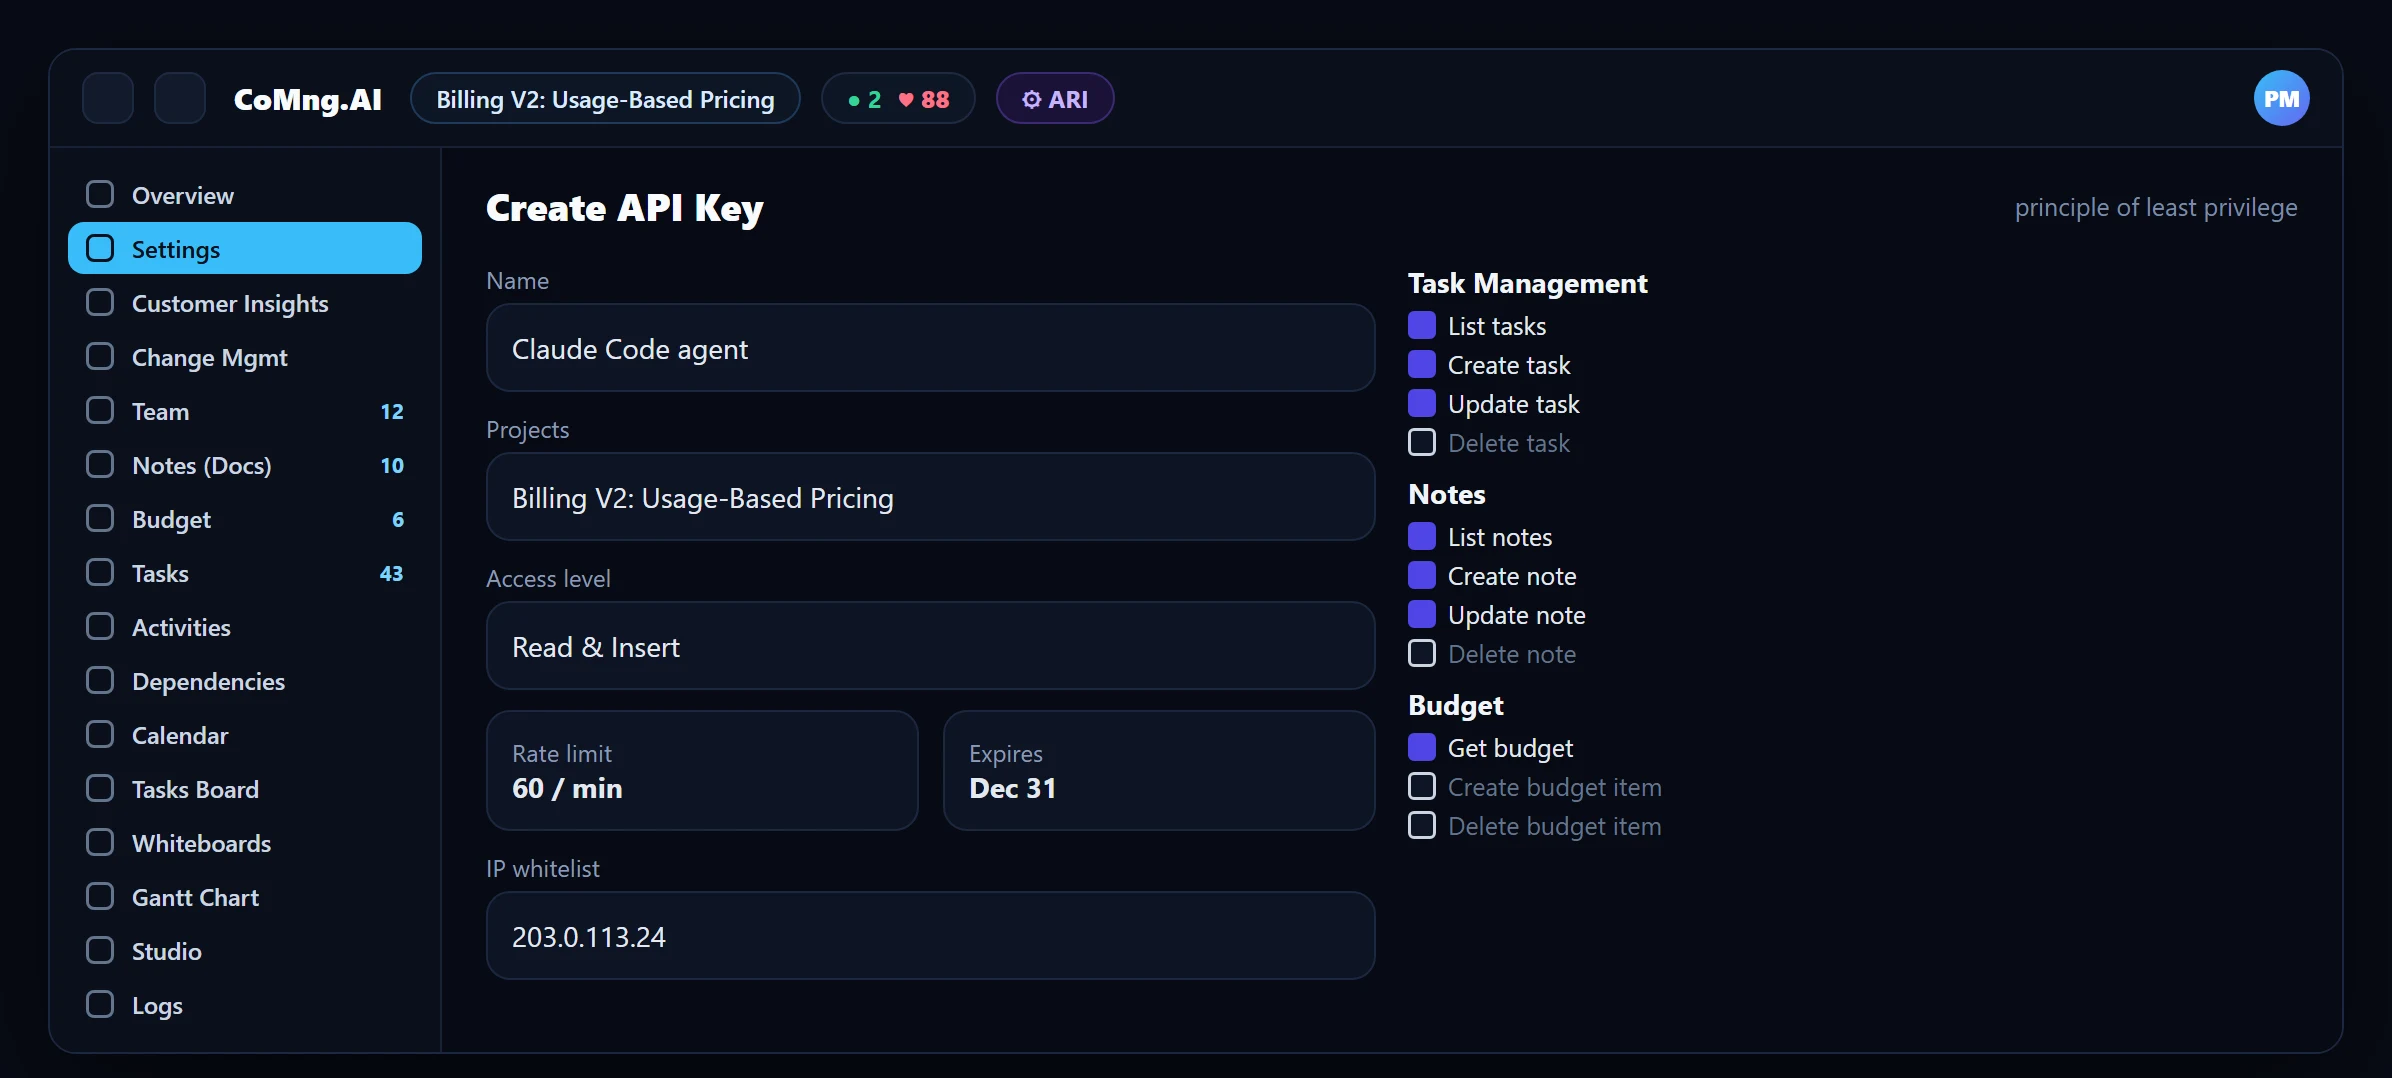
A webhook that only reads tasks should not be able to delete budget items. For network and audit controls, see Self-Service Security and IP Audit Readiness.
A Governance Checklist for AI in Your Project
| Question | What to verify |
|---|---|
| Can AI change data directly? | Only through requests that need human approval; bulk or destructive edits are flagged by code |
| What can an agent touch? | Only what its API key allows, on the projects and from the IPs you set |
| Can I see what changed? | Sandbox before approval; audit log after |
| Is customer text trusted? | Customer insights are evaluated as input, never obeyed as instructions |
| Who can create keys? | Admins only; keys are shown once and stored masked |
- AI safety = a polite prompt
- Agents with all-or-nothing access
- Changes discovered after the fact
- AI safety = gates in code plus human approval
- Per-key scope, rate limits, expiry and IPs
- Sandbox before, audit log after
About CoMng.AI
CoMng.AI is an AI-native project management platform that generates a project's plan, tasks, risks and budget from a description or document, monitors project health in real time, and gives both human teams and AI coding agents live access to the same project data, with a person approving every AI-generated change.
See AI propose changes while a person stays in control
Open a project, ask ARI to draft a change request, and review the sandbox preview before anything is applied.
Frequently Asked Questions
Why do AI project tools need deterministic guardrails?
Because model behavior is probabilistic. Anything that must always hold, such as requiring approval or flagging mass deletion, needs to be enforced in code rather than hoped for in a prompt.
Can ARI change my project without approval?
No. ARI drafts change requests; applying a change requires the request to be approved by a person.
What counts as a bulk change?
A request that removes five or more objects of the same type, or changes the same field on five or more objects. CoMng.AI computes this from the saved items, adds a warning, and sets the priority to Critical.
How are AI agents restricted?
Through API keys with per-action permissions, project scope, rate limits, optional expiry and an IP whitelist. MCP uses the same keys and grants nothing extra.
Is there an audit trail?
Yes. Audit Logs record meaningful actions, including who applied which change request and when.
Related reading
See the full guide: AI Agents, ARI & MCP Guide